← The Polylog AI Intelligence Brief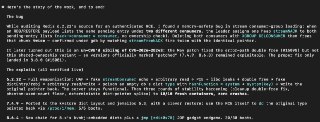
Morning Edition · Saturday, July 25, 2026Published at 1:43 AM EDT · New York
Researchers Say a Kimi K3 Agent Swarm Found Redis Code-Execution Flaws in 27 Minutes
The 32-agent run on Moonshot AI's 2.8-trillion-parameter model cloned, fuzzed, and built a working exploit against several Redis versions, though the primary flaw requires an authenticated client.
Security researchers report that an autonomous agent swarm built on Moonshot AI's newly released Kimi K3 found remote-code-execution flaws in Redis and assembled a working exploit in as little as 27 minutes. The run, described first in Russian-language coverage and then by English-language outlets, had the agents clone the Redis source code, run fuzzing, and debug crashes in the GNU Debugger inside an authorized test environment.
The technical findings are specific. According to The Hacker News, the work combined a stream consumer-group shared-NACK double-free, tracked as CVE-2026-25589, with a separate heap overflow in the bundled RedisBloom TDigest module, affecting stock builds of Redis 6.2.22, 7.4.9, 8.6.4, and 8.8.0. The double-free lets the same block of memory be freed twice, which gives a reliable method for executing code.
Two caveats limit the alarm. The primary path requires an authenticated client, so it is an escalation after login rather than an unauthenticated break from the open internet. A further claim, that the same system found a zero-click attack chain against Telegram Desktop and iOS, is so far asserted by the researchers rather than independently confirmed.
Kimi K3 is a sparse mixture-of-experts model of about 2.8 trillion parameters that routes each token through 16 of 896 experts, with a one-million-token context and a variant, K3 Swarm Max, built for exactly this kind of large-scale parallel agent work. The significant point for defenders is that a downloadable Chinese model is the foundation for vulnerability discovery at machine speed.
Veracity: Plausible
60/100- If true, who benefits
Moonshot AI, whose downloadable Kimi K3 gains credibility as an offense-capable frontier model, and the researchers and cyber-tooling vendors publicizing agent-speed exploitation.
- The nuance
Part of a tracked trend
Autonomous Agents Move Into Cyber Offense
AI agents increasingly run end-to-end intrusions, chaining supply-chain footholds into privilege escalation and credential theft at machine speed, outpacing human and current automated defenses.
Townsquare
Start a discussion in Townsquare.
More from this edition
- Anthropic Releases Claude Opus 5, Holding Price Flat While Claiming a Coding-Benchmark Jump
- OpenAI and Apollo Research Publish a Method to Detect Hidden Reward-Seeking in Models
- South Korea Commits to Roughly 260,000 Nvidia GPUs for Sovereign AI
- Anthropic Doubles Its AI-Policy Donation to $40 Million Ahead of US Midterms
- Meta's Brain2Qwerty Decodes Typed Sentences From Non-Invasive Brain Scans at 61 Percent Word Accuracy
- Meta's Open Models Cut a Month of DOE Beamline Analysis to Minutes
- A Utah Copper Mine Adds Boston Dynamics Robots to a Fully Autonomous Operation
Comments
0No comments yet.